Loading...
Searching...
No Matches
Tls.h File Reference
This graph shows which files directly or indirectly include this file:

Go to the source code of this file.
Classes | |
| struct | TlsSessionCallbacks |
| struct | __TlsSession |
Typedefs | |
| typedef STATUS(* | TlsSessionOutboundPacketFunc) (UINT64, PBYTE, UINT32) |
| typedef VOID(* | TlsSessionOnStateChange) (UINT64, TLS_SESSION_STATE) |
| typedef struct TlsSessionCallbacks * | PTlsSessionCallbacks |
| typedef struct __TlsSession | TlsSession |
| typedef struct __TlsSession * | PTlsSession |
Enumerations | |
| enum | TLS_SESSION_STATE { TLS_SESSION_STATE_NEW , TLS_SESSION_STATE_CONNECTING , TLS_SESSION_STATE_CONNECTED , TLS_SESSION_STATE_CLOSED } |
Functions | |
| STATUS | createTlsSession (PTlsSessionCallbacks, PTlsSession *) |
| STATUS | freeTlsSession (PTlsSession *) |
| STATUS | tlsSessionStartWithHostname (PTlsSession, BOOL, PCHAR) |
| STATUS | tlsSessionStart (PTlsSession, BOOL) |
| STATUS | tlsSessionProcessPacket (PTlsSession, PBYTE, UINT32, PUINT32) |
| STATUS | tlsSessionPutApplicationData (PTlsSession, PBYTE, UINT32) |
| STATUS | tlsSessionShutdown (PTlsSession) |
| STATUS | tlsSessionChangeState (PTlsSession, TLS_SESSION_STATE) |
Typedef Documentation
◆ PTlsSession
| typedef struct __TlsSession * PTlsSession |
◆ PTlsSessionCallbacks
| typedef struct TlsSessionCallbacks * PTlsSessionCallbacks |
◆ TlsSession
| typedef struct __TlsSession TlsSession |
◆ TlsSessionOnStateChange
| typedef VOID(* TlsSessionOnStateChange) (UINT64, TLS_SESSION_STATE) |
◆ TlsSessionOutboundPacketFunc
| typedef STATUS(* TlsSessionOutboundPacketFunc) (UINT64, PBYTE, UINT32) |
Enumeration Type Documentation
◆ TLS_SESSION_STATE
| enum TLS_SESSION_STATE |
Function Documentation
◆ createTlsSession()
| STATUS createTlsSession | ( | PTlsSessionCallbacks | pCallbacks, |
| PTlsSession * | ppTlsSession ) |
Create TLS session. NOT THREAD SAFE.
- Parameters
-
PTlsSessionCallbacks - callbacks PTlsSession* - pointer to created TlsSession object
- Returns
- STATUS - status of operation
Here is the call graph for this function:

Here is the caller graph for this function:

◆ freeTlsSession()
| STATUS freeTlsSession | ( | PTlsSession * | ppTlsSession | ) |
Free TLS session. Not thread safe.
- Parameters
-
PTlsSession - TlsSession object to free
- Returns
- STATUS - status of operation
Here is the call graph for this function:

Here is the caller graph for this function:

◆ tlsSessionChangeState()
| STATUS tlsSessionChangeState | ( | PTlsSession | pTlsSession, |
| TLS_SESSION_STATE | newState ) |
Here is the caller graph for this function:

◆ tlsSessionProcessPacket()
| STATUS tlsSessionProcessPacket | ( | PTlsSession | pTlsSession, |
| PBYTE | pData, | ||
| UINT32 | bufferLen, | ||
| PUINT32 | pDataLen ) |
Decrypt application data up to specified bytes. The decrypted data will be copied back to the original buffer. During handshaking, the return data size should be always 0 since there's no application data yet. NOT THREAD SAFE.
- Parameters
-
PTlsSession - TlsSession object PBYTE - encrypted data UINT32 - the size of buffer that PBYTE is pointing to PUINT32 - pointer to the size of encrypted data and will be used to store the size of application data
Here is the call graph for this function:

Here is the caller graph for this function:

◆ tlsSessionPutApplicationData()
| STATUS tlsSessionPutApplicationData | ( | PTlsSession | pTlsSession, |
| PBYTE | pData, | ||
| UINT32 | dataLen ) |
Encrypt application data up to specified bytes. The encrypted data will be sent through specified callback during initialization. If NULL is specified, it'll only check for pending handshake buffer. NOT THREAD SAFE.
- Parameters
-
PTlsSession - TlsSession object PBYTE - plain data UINT32 - the size of encrypted data
Here is the call graph for this function:

Here is the caller graph for this function:

◆ tlsSessionShutdown()
| STATUS tlsSessionShutdown | ( | PTlsSession | pTlsSession | ) |
Mark Tls session to be closed NOT THREAD SAFE.
Here is the call graph for this function:

Here is the caller graph for this function:

◆ tlsSessionStart()
| STATUS tlsSessionStart | ( | PTlsSession | pTlsSession, |
| BOOL | isServer ) |
Start TLS handshake. NOT THREAD SAFE.
- Parameters
-
PTlsSession - TlsSession object BOOL - is server
- Returns
- STATUS - status of operation
Here is the call graph for this function:

◆ tlsSessionStartWithHostname()
| STATUS tlsSessionStartWithHostname | ( | PTlsSession | pTlsSession, |
| BOOL | isServer, | ||
| PCHAR | hostname ) |
Start TLS handshake with an optional hostname parameter. NOT THREAD SAFE.
- Parameters
-
PTlsSession - TlsSession object BOOL - is server PCHAR - hostname hint for TLS backends that support hostname verification or SNI, or NULL when no hostname is available. The current OpenSSL backend ignores this parameter and preserves the existing behavior.
- Returns
- STATUS - status of operation
Here is the call graph for this function:
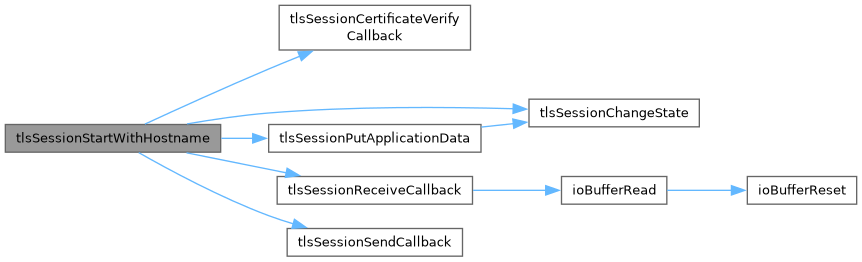
Here is the caller graph for this function:

