KNFSD-File-Cache
v1.1.0-beta.4 (September 15, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
BREAKING CHANGES: Ensure
.devcontainer/devenvironment is rebuilt if used for local development.
- Packer: Updated to Linux kernel v7.2.6-knfsd.
- Packer: Added kernel patch
0001-block-Fix-start-and-length-check-added-to-iov_iter_extract_bvecs.patch, fixingiov_iter_extract_bvecs()for theITER_FOLIOQiterators used bycachefiles. Without this, FS-Cache reads are never served from the cache and sparse source ranges are never cached. - Added a new
CACHEFILESD_EXTSIZETerraform variable (default8, allowed values0,4,8,16MiB) that applies an XFS extent size hint to the FS-Cache filesystem (/var/cache/fscache). - The extent size hint is re-applied recursively to existing cache directories when the value changes, so updating
CACHEFILESD_EXTSIZEtakes effect on the next instance boot. - Introduced a
fragmentationOpen Telemetryreceiver/componentreporting FS-Cache backing file extent statistics via theFIEMAPioctl:knfsd/fscache/extents/mean_bytes,knfsd/fscache/extents/max,knfsd/fscache/extents/unwritten_bytes, andknfsd/fscache/fragmentation/scrape_duration. Collected every 10 minutes as it requires walking the cache. - Added a new
FS-Cache Fragmentationsection to the CloudWatchmetricsdashboard with 4 widgets:FS-Cache: Mean Extents Length,FS-Cache: Max Extents per File,FS-Cache: Unwritten Capacity, andCPU per FS-Cache Read. - Updated KNFSD Monitoring Dashboard to
v16. - Added
docs/known-issues.mdentry describing FS-Cache backing file extent fragmentation, its symptoms, and the remedy. - Added
GET /api/v1/cache/statsto the KNFSD Agent, reporting theDownOps,CaRdOpsandCaWrOpscounters from/proc/fs/fscache/statsso that a cache which is written but never read can be detected. - Added
POST /api/v1/cache/dropto the KNFSD Agent, freeing the kernel caches with an optionalmodeof1,2or3(default3). - Smoke-tests: Added a
proxy serves reads from cachecheck asserting the FS-Cache read counter increases, dropping the page cache on both the client and the proxy so the re-read cannot be served from RAM. The previous check only measured cache growth, which passes even when the cache never serves a read. - Smoke-tests: Added a
proxy caches sparse source filescheck, covering buffered reads of sparse source files, which were not previously exercised as all test data was written as random bytes. - Added
AGENTS.mdfor AI coding assistant guidance (excluded from the documentation site). - Enhanced the
repo_links.pyMkDocs hook so links to unpublished or non-renderable repository files now resolve to the repository browser. - Improved the regex for matching icon/emoji shortcodes in the
cards.pyMkDocs hook to avoid exponential backtracking. - Updated
pre-commitdocumentation. - Added a
semgrepGitLab CI job to thesecuritystage. - Excluded
debug/directory frommake pylint,make black, andmake mypytargets. - Moved the Trivy cache out of the workspace. The Trivy targets now use
TRIVY_CACHE_DIR(default$HOME/.cache/trivy) instead of.trivycachein the repository root, and thedevcontainer backs that path with aknfsd-dev-trivy-cachecontainer volume. Thesetup-remote-vm.shRemote-SSH user-data script exports the same variable for consistency. GitLab CI is unchanged, as it caches.trivycacheinside the project directory. - Minor Golang package updates.
v1.1.0-beta.3 (September 7, 2026)
BROKEN: Do NOT use this release.
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
BREAKING CHANGES: Ensure
.devcontainer/devenvironment is rebuilt if used for local development.BREAKING CHANGES: Ensure
.devcontainer/prodenvironment is rebuilt if used for production.
- Packer: Updated to Linux kernel v7.2.3-knfsd.
- Packer: Updated to
amzn/amzn-driversENA driver v2.17.3 (required for Linux kernel v7.2). - Packer: The
rebootprovisioner now setsskip_cleanand a 1mtimeout, andpause_beforeon the following provisioner as per Packer documentation for handling reboots. - Fixed intermittent
mypyBus error(SIGBUS, exit code 135) failures in thedevcontainer that causedmake lintandmake pcto fail on alternating runs.mypystores its incremental cache in sqlite databases using WAL journal mode, which memory maps a*-shmfile, and that mapping faults on thevirtiofsworkspace bind mount. Thedevcontainer now setsMYPY_CACHE_DIRto aknfsd-dev-mypy-cachecontainer volume so the cache is no longer written to the workspace. Thesetup-remote-vm.shRemote-SSH user-data script exports the same variable for consistency. - Disabled IPv6 in the
devandproddevcontainers. - Set
DisableValidateResponseChecksumon theknfsd-fsiddDynamoDB test client to suppress spuriousWARN failed to close HTTP response bodymessages, asDynamoDB Localomits thex-amz-crc32header on error responses and the AWS SDK for Go v2 validates the body against a zero checksum (aws/aws-sdk-go-v2#3545). - Added
aws_iam_role_policy_attachment.lambda_static_ipto thedepends_onof thestatic_ipLambda function in thedns_round_robinmodule, so the IAM policy is attached to the Lambda role before the function is created. Previously the function and the policy attachment were created in parallel, leaving a window where EventBridge could invoke the function before its role had any permissions. - Reliability improvements to
update-pinned-versions.shscript. - Replaced the
errors.Ascalls inknfsd-fsiddandknfsd-metrics-agentwith the genericerrors.AsTypeadded in Golang v1.26, resolving the newgolangci-lintmodernizefindings. - Removed the redundant embedded field types from the
nfsStatsGroupandConfigstruct literals inknfsd-metrics-agent, resolving the newgolangci-lintmodernizeembedlitfindings enabled by Golang v1.27. - Updated to Golang v1.27.1.
- Updated to Terraform
awsprovider v6.63.0. - Updated GitHub CodeQL actions.
- Minor Golang package updates.
v1.1.0-beta.2 (August 13, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer:
v1.1.0-beta.2or later AMI is required for the new DynamoDB FSID database.BREAKING CHANGES: The external FSID database (
FSID_MODE="external") is now an Amazon DynamoDB table instead of an Amazon RDS for PostgreSQL instance.BREAKING CHANGES: The CloudWatch
metricsdashboardv15is only compatible withv1.1.0-beta.2and later.EXPERIMENTAL: SSM Session Manager support for Packer is experimental and subject to change. Using the default
SSH_INTERFACE = ""is recommended for production deployments.
- Packer: Updated to Linux kernel v7.1.8-knfsd.
- Added
mkdocsdocumentation site to the project: https://awslabs.github.io/knfsd-file-cache. - Migrated to Amazon DynamoDB from Amazon RDS for PostgreSQL. This is a breaking change. Highlights:
- Reduction in Terraform, Packer, Lambda, and
local-execprovisioner complexity, operational overhead, and operating cost. - Increased availability and durability. DynamoDB is a distributed, highly-available, regional, managed NoSQL database.
- Faster Terraform
applyanddestroytimes. - The
db-setupLambda function, Docker deployment prerequisite, andlocal-execTerraform provisioner have been removed. - Multiple Terraform variables in the
databaseandterraform-module-knfsdmodules have been removed. - The
FSID_DATABASE_CONFIGobject shape changed to{table_name, region, enable_metrics}and thedatabase_configoutput changed accordingly. - The
knfsd-fsidd[database]configuration keys changed totable-name/region(url,iam-auth, andcreate-tableremoved). - The
fsid.sql.query.*metrics were renamed tofsid.db.query.*and the CloudWatchmetricsdashboard's RDS section was replaced with a DynamoDB section. DynamoDB LocalDocker container is now used for the FSID database in thesmoke-testslocal./image/smoke-tests/test.shharness and GitLab CI instead of PostgreSQL.- Updated KNFSD Monitoring Dashboard to
v15. - Fixed the
smoke-testsbuild-remotetarget to cross-compile theremote.testbinary for the client architecture (TerraformARCH, defaultamd64) via a newTARGET_ARCHvariable, decoupling it from the devcontainer host architecture. - Added an optional VPC Endpoints Terraform module (deployment/vpc-endpoints) for deploying the AWS PrivateLink interface endpoints and DynamoDB gateway endpoint required to run KNFSD in a private subnet without internet connectivity.
- Added
EXISTING_SECURITY_GROUP_IDandEXISTING_INSTANCE_PROFILE_NAMEvariables to theterraform-module-knfsdmodule (both default""). When set, the module skips creating the ASG security group (and all ingress/egress rules) and/or the IAM role, instance profile, and associated policies, using the pre-created resources instead. This supports deployment under restrictive IAM roles that denyec2:CreateSecurityGroupand/oriam:CreateRole/iam:CreatePolicy. A singleEXISTING_SECURITY_GROUP_IDserves both the ASG and the Network Load Balancer inloadbalancermode. - Added
EXISTING_LAMBDA_ROLE_ARNvariable to thedns_round_robinmodule (default"") to reuse a pre-created IAM role for thestatic_ipLambda function instead of creating one. - Added
EXISTING_SECURITY_GROUP_IDvariable to thevpc-endpointsmodule (default""). When set, the module skips creating the interface-endpoint security group and its ingress/egress rules, attaching the provided security group instead. This supports deployment under restrictive IAM roles that denyec2:CreateSecurityGroup. - Extended
FSID_DATABASE_IAM_POLICYso it can also be set whileFSID_DATABASE_DEPLOY=true. The DynamoDB table is still deployed, but thedatabasemodule skips creating the DynamoDB accessaws_iam_policyand the provided policy is attached to the KNFSD instance role instead. This supports deployment under restrictive IAM roles that denyiam:CreatePolicywhile still provisioning the table. - Added an
instance_profile_nameoutput to theterraform-module-knfsdmodule that always returns the instance profile name (created or user-provided).iam_role_namenow returnsnull(omitted fromterraform output) whenEXISTING_INSTANCE_PROFILE_NAMEis set. - Changed the Auto Scaling and Elastic Load Balancing service-linked role handling to a read-only
iam:ListRolespre-flight check that fails early duringterraform planwith a clear message and CLI remedy if a required role is missing, replacing the previouslocal-execprovisioner that shelled out toaws iam create-service-linked-role. TheAWSServiceRoleForAutoScalingrole is always required;AWSServiceRoleForElasticLoadBalancingis required only inloadbalancerTRAFFIC_MODE. - Removed
iam:CreateServiceLinkedRolefrom the required/optional Terraform IAM policies (docs/iam/tf-required.json, docs/iam/tf-optional.json), replacing it withiam:ListRolesfor the read-only pre-flight checks. - Documented the manual
aws iam create-service-linked-rolestep (forspot.amazonaws.com,fsx.amazonaws.com,autoscaling.amazonaws.com, andelasticloadbalancing.amazonaws.com) across the Packer image/README.md, theexamples/*READMEs, docs/iam.md, and docs/security-considerations.md for accounts using centrally-managed IAM. - Added a self-contained docs/iam/vpc-endpoints.json IAM policy for the standalone
vpc-endpointsmodule (VPC endpoints, security group, networking lookups, and its CloudFormation metrics stack), removing the staleKnfsdVpcEndpointsSid from docs/iam/tf-optional.json. - Reconciled docs/iam.md: removed the stale
KnfsdAsgServiceLinkedRolerow (superseded by theiam:ListRolespre-flight check), documented the newvpc-endpoints.jsonpolicy, and added a "Deploying under restrictive IAM" section mapping eachEXISTING_*variable to the create-permissions it lets you drop. - Packer: Added optional AWS SSM Session Manager support to the Packer AMI build via a new
SSH_INTERFACEvariable (default"", unchanged SSH behaviour). SettingSSH_INTERFACE = "session_manager"tunnels the build connection over AWS Systems Manager, allowing the AMI to be built in a private subnet with no inbound SSH, no public IP address, and no bastion host. This mode requiresIAM_INSTANCE_PROFILEto be set and the AWSsession-manager-pluginto be installed locally. When enabled, the temporary security group is created without any ingress rule andhttps://checkip.amazonaws.comis no longer contacted (#37). - Packer: Added the
KnfsdPackerSsmChannels,KnfsdPackerSsmStartSession, andKnfsdPackerSsmManageSessionSids to docs/iam/packer.json so a single policy covers both Packer connection methods, plus a new standalone docs/iam/packer-instance-profile.json least-privilege policy for the Packer build instance's own IAM role (AWS SSM agent registration, andec2:CreateTagsforTAG_BUILD_STATUS). docs/iam.md documents which Sids can be dropped when standardizing on one connection method, along with the trust policy andaws iamcommands to pre-create the instance profile under restrictive IAM environments. - Packer: Split the
rebootthat follows10_build.shinto its own provisioner so the main build provisioner no longer setsexpect_disconnect, and removedexpect_disconnectfrom the30_finalize.shprovisioner. A connection lost during the build or finalize step (for example an EC2 Spot reclaim) now fails the build immediately instead of being treated as a completed provisioner, which could previously truncate the build silently. - Packer: Fixed the documented security group precedence so that setting both
SECURITY_GROUP_IDandSECURITY_GROUP_IDSnow honoursSECURITY_GROUP_IDas documented, instead of failing with "Only one of security_group_id or security_group_ids can be specified". - Remote-SSH: Added optional AWS SSM Session Manager support to the developer cloud development environment via a new
KNFSD_REMOTE_SSH_TUNNELenvironment variable (defaulteice, unchanged behaviour). SettingKNFSD_REMOTE_SSH_TUNNEL=ssmtunnels the SSH connection for.devcontainer/dev/remote.shover AWS Systems Manager using theAWS-StartSSHSessiondocument. - Remote-SSH: Added the same optional AWS SSM Session Manager support to
.devcontainer/dev/run-fio-nfs.shvia a new--tunnel <eice|ssm>option on theruncommand (defaulteice, unchanged behaviour). - Remote-SSH: Added a new standalone docs/iam/remote-ssh.json least-privilege policy for the developer identity running
remote.shorrun-fio-nfs.sh, plus docs/iam/remote-ssh-instance-profile.json for the development instance's own IAM role (AWS SSM agent registration, andec2:CreateTagsfor the readiness tag). - Scoped the KNFSD instance role's
ssm:GetParametersByPathIAM policy to the deployment's own parameter hierarchy (/knfsd/<cluster-name>and/knfsd/<cluster-name>/*) instead of the account-wide/knfsd/*, and added the path-level ARN thatGetParametersByPathauthorizes against (#41). - Made
knfsd-file-cache:statustagging inproxy-startup.shbest-effort so an unreachable EC2 API no longer aborts proxy startup. The first failedec2:CreateTagscall disables tagging for the remainder of that boot, logs the remedy, and startup continues. Also hardened the critical SSM Parameter Store load to fail fast with an actionable message instead of aborting on a raw connection timeout, and to reject a successful call that returns zero parameters (#39). - Removed unnecessary fs-cache mount options from
proxy-startup.sh. - Added a new
basicNFS example to theexamples/directory to demonstrate the minimal KNFSD deployment. See examples/basic/README.md for details. - Added shell tooling to update pinned version dependencies in the project:
update-pinned-versions.shandupdate-github-action-shas.sh. - Enhanced
.devcontainer/dev/query-regions-for-ec2-instance-type.shwith ausage()message (printed for no arguments or-h/--help), a new-r/--regionflag to query the AZs of a single AWS region, and an end-of-run summary table of the AZ and region totals, listing every region queried and its AZs grouped by full, partial, or no availability. - Updated
BATSto v1.14.0. - Updated to Packer v1.16.0.
- Updated to Terraform
awsprovider v6.59.0. - Updated to Python v3.14.7.
- Updated GitHub CodeQL actions.
- Minor Golang package updates.
v1.1.0-beta.1 (July 17, 2026)
BREAKING CHANGES: Ensure
.devcontainer/devenvironment is rebuilt if used for local development.BREAKING CHANGES: Ensure
.devcontainer/prodenvironment is rebuilt if used for production.
- Fixed
tflintinheritance issue in GitLab CI andMakefileconfiguration by settingTFLINT_CONFIG_FILEenvironment variable. - Fixed typo in
terraform-module-knfsdREADME.mdandvariables.tf.TRAFFIC_MODEis no longer a required (now optional) Terraform variable. - Switched
devcontainerdefault architecture fromamd64toarm64. See docs/developer.md if you need to forceamd64instead. - Fixed the
smoke-testsbuild-remotetarget to cross-compile theremote.testbinary for the client architecture (TerraformARCH, defaultamd64) via a newTARGET_ARCHvariable, decoupling it from the devcontainer host architecture. - Added GitLab CI configuration for running
smoke-testsCI jobs. - Added
TRIVY_DISABLE_VEX_NOTICEenvironment variable to disable VEX notices from Trivy security scans. - Updated to Terraform
awsprovider v6.55.0. - Packer: Updated
hashicorp/packer-plugin-amazonto v1.8.2. - Minor Golang package updates.
v1.1.0-alpha.29 (July 9, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Packer: Updated to Linux kernel v7.1.3-knfsd.
- Packer: Updated to
amzn/amzn-driversENA driver v2.17.2. - Packer: Added
TAG_BUILD_STATUSvariable (defaultfalse) to gate build-instance status tagging via theknfsd-file-cache:statusAWS tag. When enabled, requires Packer variableIAM_INSTANCE_PROFILEto be set to an IAM role grantingec2:CreateTags. - Updated to Golang v1.26.5.
- Updated to Terraform
awsprovider v6.53.0. - Minor Golang package updates.
v1.1.0-alpha.28 (July 1, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
BREAKING CHANGES: Ensure
.devcontainer/devenvironment is rebuilt if used for local development.BREAKING CHANGES: Ensure
.devcontainer/prodenvironment is rebuilt if used for production.
- Packer: Updated to Ubuntu 26.04 LTS (Resolute Raccoon).
- Packer: Updated to Linux kernel v7.1.2-knfsd.
- Packer: Removed unused
image.manifest.jsonandimage-name.shfile from build process. - Packer: Added additional EC2 instance types to the AMI build process to increase build capacity and reduce build time.
- Packer:
aws-clinow installed viasnap. - Packer: Added
knfsd-file-cache:statusAWS tag support to the AMI build instance to track the individual build steps. - Packer: Added
MAKE_VERBOSITYenvironment variable to build scripts to reducemakecompiler output to warnings/errors/summary. - Packer: Added
error-cleanup-provisionertoknfsd.pkr.hclto tag the build instance withknfsd-file-cache:status=failed: build errorwhen the build process fails. - Packer: Disabled irrelevant Linux kernel build targets to reduce build time and snapshot size.
- Smoke-tests: Updated to use
m6i.2xlargeEC2 instance type for the test client. - Smoke-tests: Improved error handling and logging in the smoke-test driver.
- Smoke-tests: Surface the Golang smoke-test results in the smoke-test driver output.
- Enhanced security considerations and smoke-tests documentation with additional IAM policies and variable details.
- Minor Golang package updates.
v1.1.0-alpha.27 (June 27, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
BREAKING CHANGES: All CW/OTEL logs/metrics now use the
/knfsd/logs,/knfsd/ec2, and/knfsd/metricsnamespaces (all now prefixed with a leading/).BREAKING CHANGES: The CloudWatch
metricsdashboardv14is only compatible withv1.1.0-alpha.27and later.EXPERIMENTAL: The
smoke-testsmodule is experimental and subject to change.
- Packer: Updated to Linux kernel v7.0.13-knfsd.
- Changed all CloudWatch/Open-Telemetry log/metrics group names to use the
/knfsd/logs,/knfsd/ec2, and/knfsd/metricsnamespaces (all now prefixed with a leading/). - Removed the
testing/directory and all related code. - Migrated the
image/smoke-testsmodule to AWS. It now uses SSH-over-SSM to reach the test instances:ssh/scptunnel through AWS Systems Manager (AWS-StartSSHSessionviasession-manager-plugin) and authenticate with a short-lived key pushed via EC2 Instance Connect immediately before each connection. See smoke-tests/README.md for details. - Added AWS SSM
session-manager-pluginto.devcontainer/devand.devcontainer/prodconfigurations to support running thesmoke-testsmodule. - Added AWS Session Manager Plugin to
prerequisites.mddocumentation. - Added docs/iam/testing.json documenting the test-harness IAM permissions (SSH-over-SSM + EC2 Instance Connect, scoped per resource) used by the
image/smoke-testsdriver, and documented it in docs/iam.md. - Added new Terraform variable
ASSOCIATE_PUBLIC_IP_ADDRESStoterraform-module-knfsdto allow forcefully associating (or suppressing) a public IPv4 address on the proxy EC2 instances via the launch template'snetwork_interfacesblock. Defaults tonull(inherits the subnet'sMapPublicIpOnLaunchattribute, preserving prior behavior). See deployment/README.md. - Tuned
configure_network()inproxy-startup.shfor ENA-X high-latency (inter-AZ) conditions: raised socket buffer defaults (net.core.rmem_default/wmem_default) to 4 MB, increasedtcp_limit_output_bytesfrom 1 MB to 4 MB, disabledtcp_autocorkingto reduce latency for request-response workloads, and explicitly settcp_congestion_controltocubic. - Packer: Reverted change by Canonical preventing ENA driver from being built as a
module, blocking it from being upgradable later in the AMI build process. - Packer: Fixed
rm -rf /var/lib/apt/lists/*syntax error in20_post_build.shscript. - Enhanced Packer and Terraform variable validation checks to provide more detailed error messages and improve user experience.
- Added support for AWS GovCloud regions (
us-gov-east-1andus-gov-west-1). - Added support for AWS China regions (
cn-north-1andcn-northwest-1). - Added docs/security-considerations.md documentation.
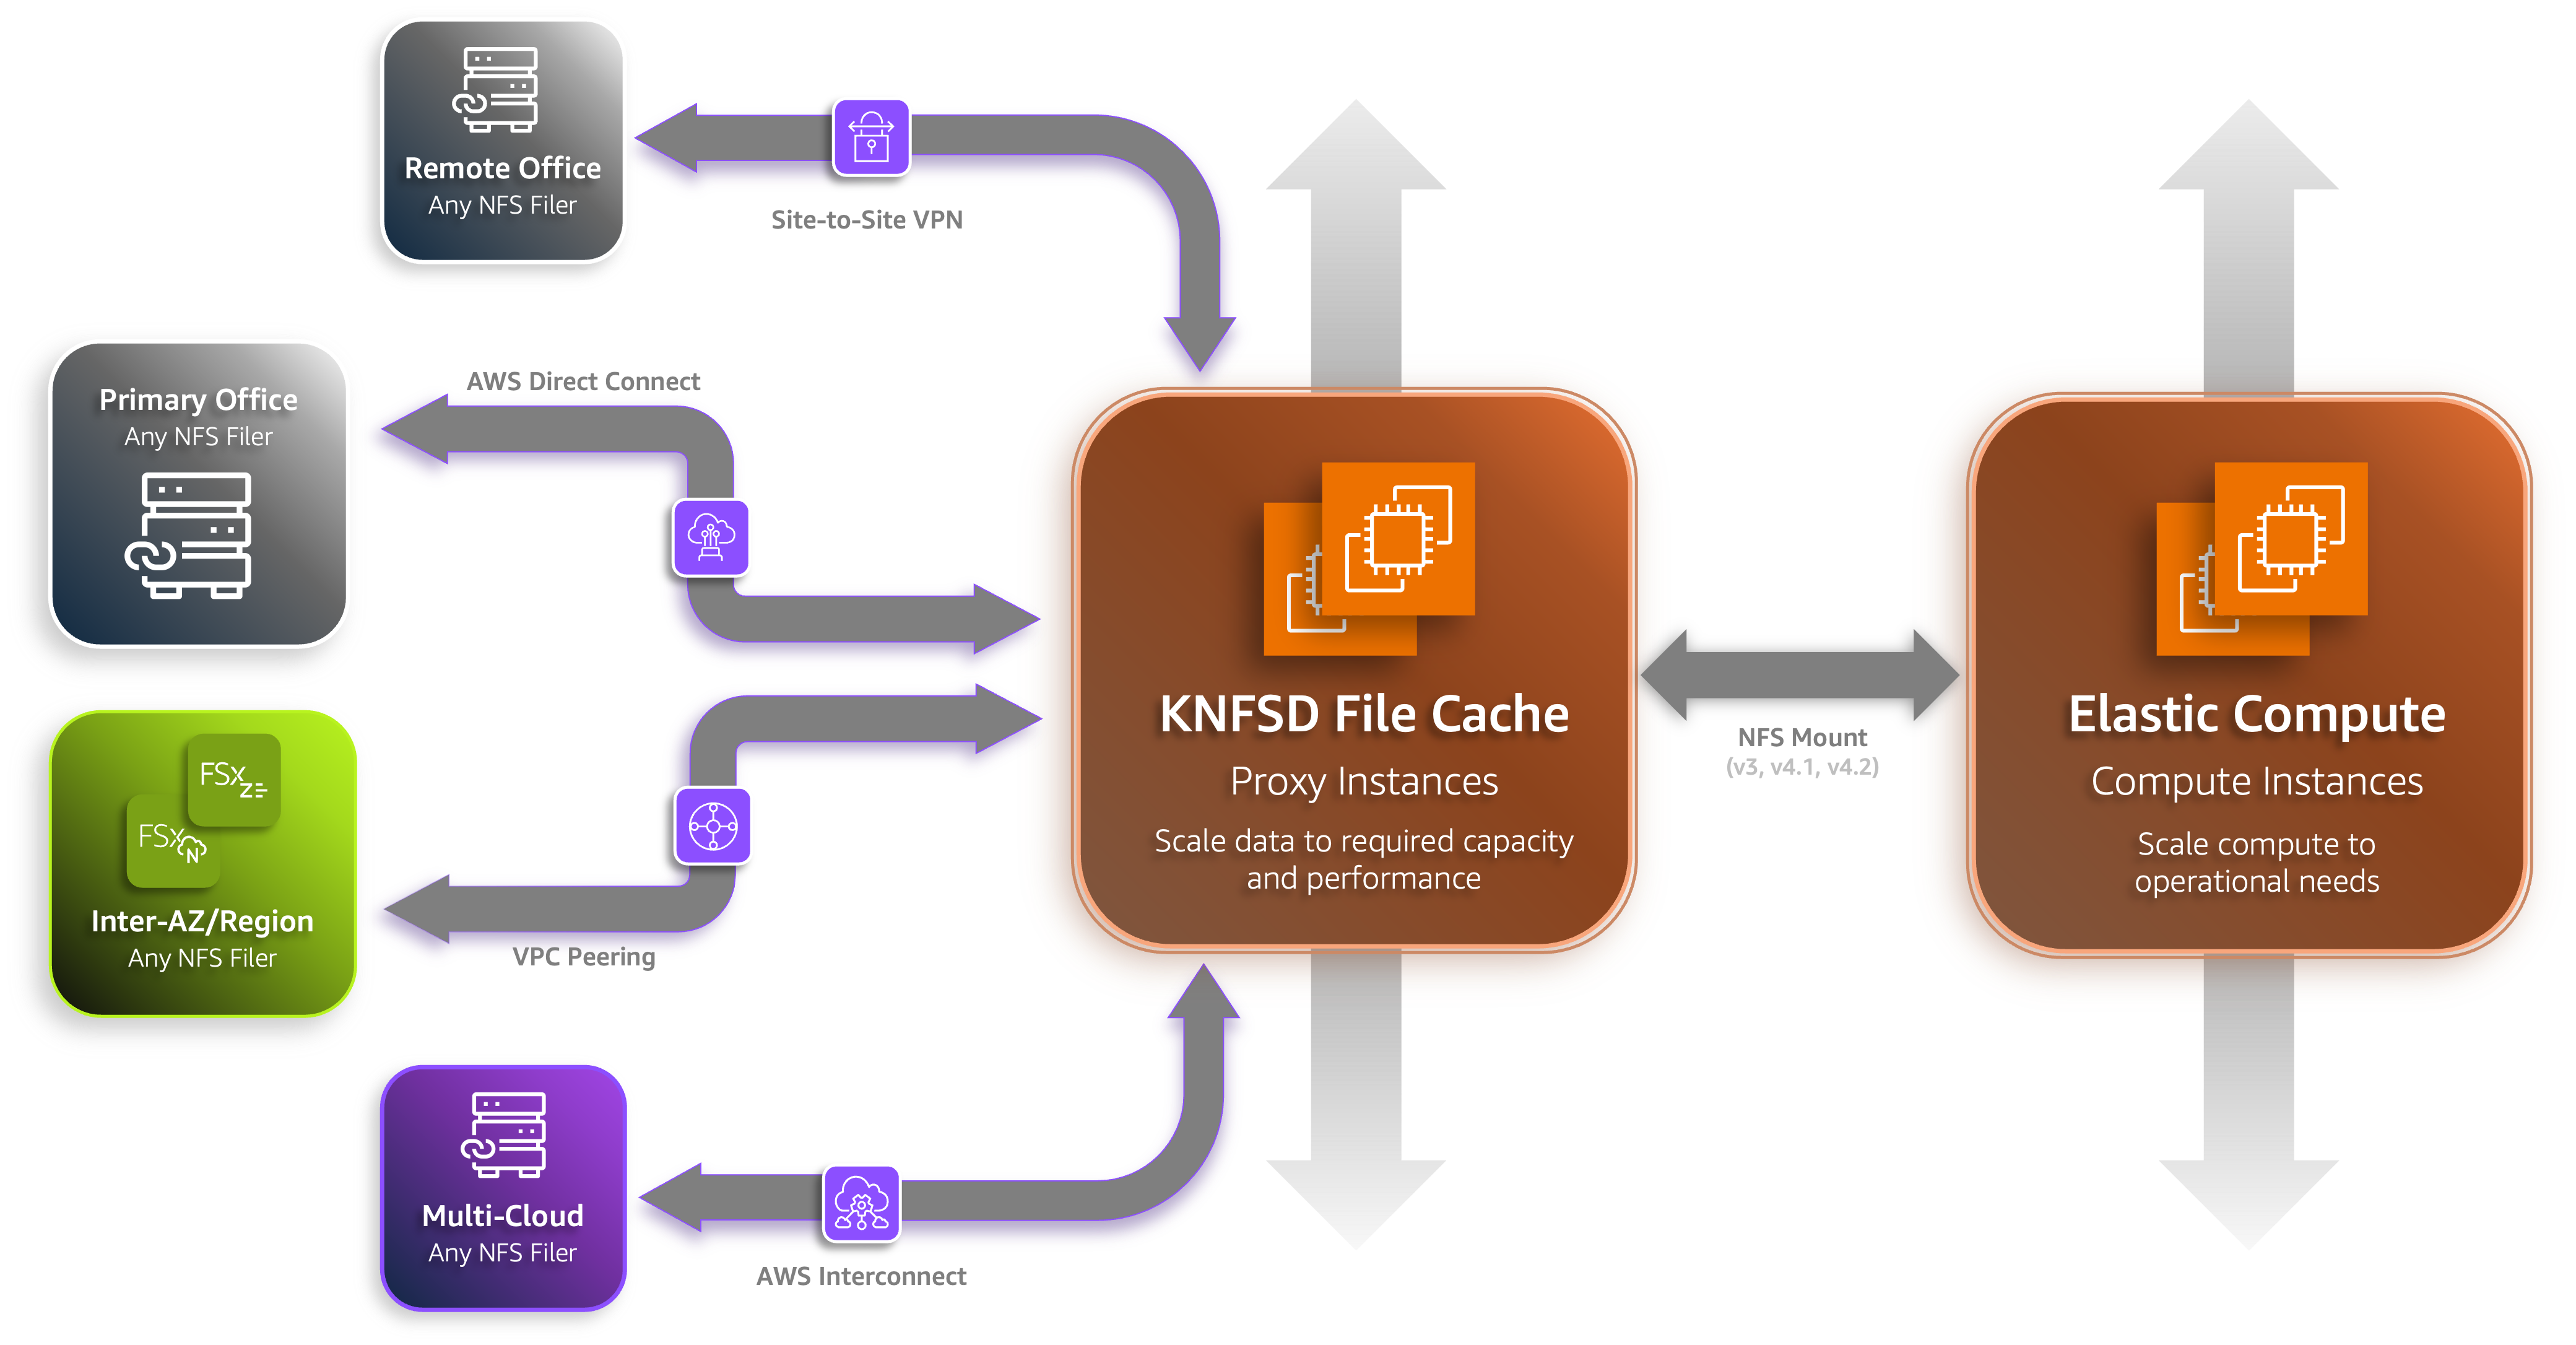
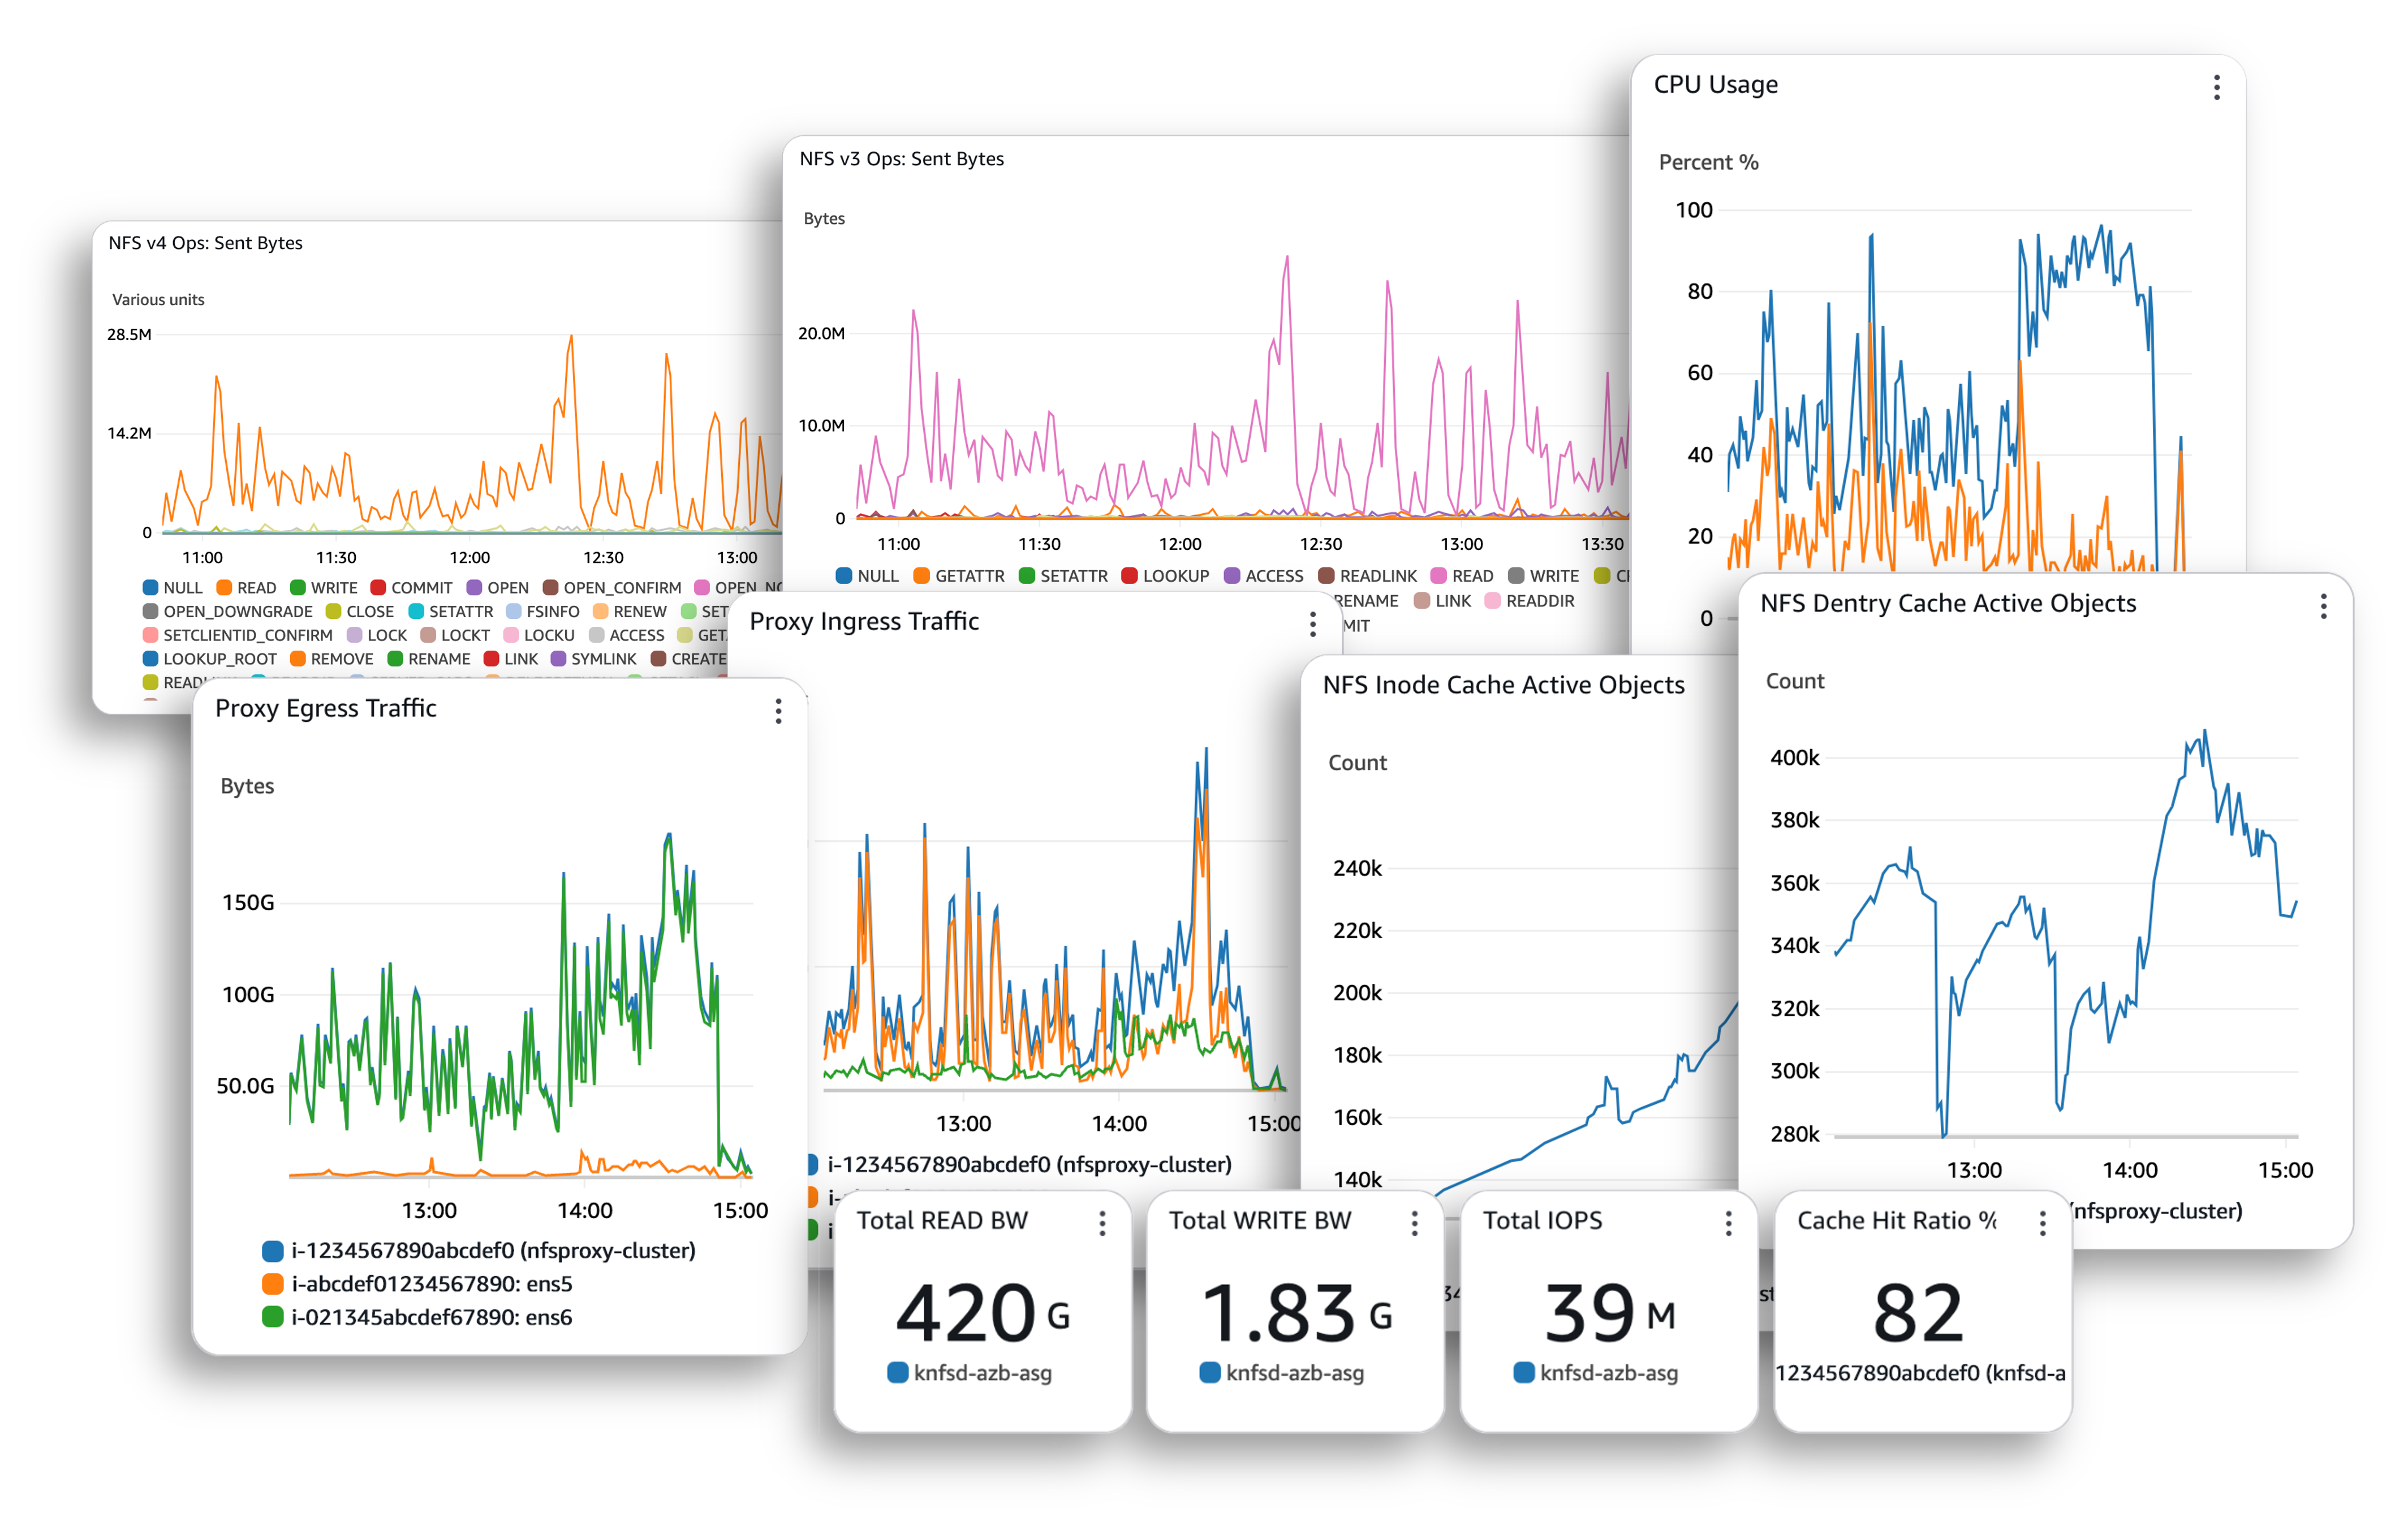
- Added docs/images/arch.png and docs/images/metrics.png images to README.
- Added
.trivy.tfvarsfile to Makefile and GitLab CI configuration for Trivy security scanning. - Removed
efsands3-filesexamples and related code from project. - Added support for 'linking' pattern variables in CloudWatch
metricsdashboard by Auto Scaling Group (ASG) Name and Instance ID. Instance ID(s), Source NFS Filer, and Output NFS Filer filters are now filtered by the currently selected Auto Scaling Group (ASG) Name. - Updated KNFSD Monitoring Dashboard to
v14. - Added inline comments for auto-discovery of exports via
showmount -e <WEKA_NFS_GATEWAY>inexamples/wekaTerraform example. EXPORT_HOST_AUTO_DETECTnow skips any individual auto-detected NFS export that cannot be mounted after the existing 3 retries, instead of aborting the entire KNFSD proxy startup. This handles NFS servers that advertise an unmountable pseudo-root/viashowmount -e. A new guard fails the proxy (exit 1) only when zero NFS exports are mounted. See docs/known-issues.md.- Added 11 BATS tests for
proxy-startup.shscript:export-auto-detect.bats. - Added FAQ entry for SSH
Permission denied (publickey)when connecting to a proxy instance. - Enhanced EC2 instance type validation and added region exclusion feature in query script:
.devcontainer/dev/query-regions-for-ec2-instance-type.sh. - Improved logging in
.devcontainer/dev/find_temp_files.shscript. - Packer: Updated
hashicorp/packer-plugin-amazonto v1.8.1. - Packer: Updated to
amazon-ec2-net-utilsv2.7.3. - Updated to Terraform
awsprovider v6.52.0. - Updated to Golang v1.26.4.
- Updated to PostgreSQL v18.4.
- Updated to Packer v1.15.4.
- Updated to Python v3.14.6.
- Minor Golang package updates.
v1.1.0-alpha.26 (May 12, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Packer: Updated to Linux kernel v7.0.6-knfsd.
- Added support for customer-managed KMS keys for AMI encryption, AMI cross-region distribution, and EBS volume encryption.
- Packer: Added new Packer variables for AMI encryption and cross-region distribution:
KMS_KEY_ID,AMI_ENCRYPTED,DISTRIBUTION_REGIONS, andREGION_KMS_KEY_IDS. See image/README.md for usage and the three supported encryption modes (defaultaws/ebs, customer-managed key, unencrypted). Customer-managed KMS keys and key policies are the customer's responsibility and not created or managed by this project. - Packer: Added
ec2:CopyImage,ec2:CopySnapshot, andec2:DeregisterImageto docs/iam/packer.json (KnfsdPackerBuildSid) to support cross-region AMI distribution. - Added new Terraform variable
EBS_KMS_KEY_IDtoterraform-module-knfsdfor customer-managed encryption of launch-template EBS volumes. Volumes remain encrypted by default; when empty, AWS uses the account's defaultaws/ebskey. See deployment/README.md. - Added no-op
Helper()method totestRunnerintesting/examples/testing/runner.goto satisfy theHelper()method now required byterratest.TestingT(added upstream in Terratest v1.0.0). - Updated
opentelemetry-collectorto v0.152.0. - Updated
opentelemetry-collector-contribto v0.152.0. - Renamed
metricstransformprocessor tometrics_transformas per Open Telemetry Collector Contrib issue #45339. - Updated to Golang v1.26.3.
- Updated to Python v3.14.5.
- Minor Golang package updates.
v1.1.0-alpha.25 (May 7, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
BREAKING CHANGES: Project-wide naming alignment from
nfsproxyandnfs-proxytoknfsd.
- Packer: Updated to Linux kernel v7.0.4-knfsd.
- Renamed
nfs-proxy.pkr.hcltoknfsd.pkr.hclinpacker/imagedirectory. - Changed
PROXY_BASENAMEdefault fromnfsproxytoknfsdinterraform-module-knfsdand allexamples/*/variables.tf. - Changed database module
NAME_PREFIXdefault fromfsidstoknfsd-fsids. - Renamed user-facing module outputs:
nfsproxy_loadbalancer_ipaddress→loadbalancer_ipaddressandnfsproxy_security_group_id→knfsd_security_group_id. - Removed
nfsproxy_loadbalancer_dnsaddressoutput from*/outputs.tfas duplication ofdns_nameoutput. - Renamed internal Terraform resource addresses (
aws_security_group.nfsproxy_*→knfsd_*,aws_launch_template.nfsproxy_template→knfsd_launch_template,aws_lb.nfsproxy_lb→knfsd_lb,aws_lb_target_group.nfsproxy_lb_tg→knfsd_lb_tg,aws_route53_zone.nfsproxy→knfsd, etc). - Added new project-wide IAM reference at
docs/iam.mdand the canonical IAM policy files underdocs/iam/:packer.json(Packer AMI build),tf-required.json(always-required deploy Sids), andtf-optional.json(feature-gated deploy Sids). - Updated
deployment/docs/vpc-endpoints.mdwith runtime-only scope, added missingec2messagesinterface endpoint, and added cross-region interface endpoints for IAM (com.amazonaws.iam) and Route 53 (com.amazonaws.route53) inus-east-1per the November 2025 AWS PrivateLink cross-region announcement. - Replaced the inline IAM policy example in
image/README.mdwith a pointer todocs/iam.mdanddocs/iam/packer.json. - Fixed regression introduced in
v1.1.0-alpha.24where theterraform-module-knfsdmodule rejectedFSID_DB_SUBNET_GROUP_NAME/FSID_DB_SUBNET_IDSin multi-AZ deployments where sibling modules consume an existing FSID database viaFSID_DATABASE_CONFIG. - Added
iamlivetool to.devcontainer/devenvironment for creating IAM policies. - Exposed
TRAFFIC_MODETerraform variable to thefsx-zfsexample. - Set default value for
TRAFFIC_MODETerraform variable todns_round_robin. - Packer: Added
snap_refreshfunction to10_build.shscript to retrysnap refreshcommands up to 5 times with a 10-50s delay between attempts to guard against transient "unable to contact snap store" errors fromapi.snapcraft.io. - Updated KNFSD Monitoring Dashboard to
v13. - Packer: Updated to
amzn/amzn-driversENA driver v2.17.0. - Packer: Updated to
amazon-efs-utilsv3.1.1. - Updated to Packer v1.15.3.
- Updated to Terraform
awsprovider v6.44.0. - Minor Golang package updates.
v1.1.0-alpha.24 (April 23, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
BREAKING CHANGES: Ensure
.devcontainer/devenvironment is rebuilt if used for local development.EXPERIMENTAL: Amazon S3 Files (
s3files) support is experimental and subject to change.
- Packer: Updated to Linux kernel v6.19.14-knfsd.
- Updated
opentelemetry-collector-contribto v0.150.0 to fix bugs inexporter/awsemf: Fix data races ingetPusherandlogPusherthat cause nil pointer panics and out-of-order log events (#47126) - Added support for EC2 Instance Bandwidth Configuration (bandwidth weighting). Only certain EC2 instance types support this feature; when the instance type is detected as supported, the configuration is applied automatically. This can increase network bandwidth available to the instance by up to 25% (at the cost of reduced baseline EBS bandwidth for the same instance).
- Added support for ENA Express (ENA-X), which is automatically enabled when the selected EC2 instance type for the KNFSD instance supports it. ENA Express can raise maximum single-flow bandwidth from 5 Gbps to 25 Gbps for NFS traffic between instances in the same Availability Zone, up to the instance’s aggregate network limit. Both TCP and UDP will use ENA-X. The sending and receiving instances (KNFSD instance and NFS client instances) must both support ENA-X for it to be enabled. If any requirement is unmet, traffic falls back gracefully to standard TCP/UDP without ENA-X.
- Added ENA-X support to secondary ENI attachment via Lambda
static_ipfunction indns_round_robinmodule. - Added
configure_network()function toproxy-startup.shthat tunes the Linux network stack and ENA driver on every boot for high-throughput NFS proxy traffic. Kernel-level changes include raising socket buffer ceilings (rmem_max/wmem_max) to 16 MB, increasingnetdev_max_backlogto 16384, widening TCP auto-tuning ranges to 16 MB, and raisingtcp_limit_output_bytesto 1 MB for ENA-X. Per-ENA-interface tuning sets MTU to 8900, Rx ring buffers to 8192, enables adaptive Rx interrupt coalescing, and configures Receive Packet Steering (RPS) across all vCPUs to distribute softirq processing evenly. - Replaced manual sysfs-based
configure_read_ahead()function inproxy-startup.shwith declarative[nfsrahead]configuration in/etc/nfs.conf.d/knfsd.conf. Readahead is now applied automatically via thenfsraheadudev tool to all NFS mounts, includingautofs-triggered nested mounts. Amazon Elastic File System (EFS) mounts are unaffected asefs-utilsoverwritesread_ahead_kbafter mount. - [EXPERIMENTAL] Added Amazon S3 Files (
s3files) filesystem type support inproxy-startup.sh. Thes3filesmount helper (mount.s3files) is now handled identically tomount.efs:nconnectis stripped and the mount helper's own retry logic is used (single attempt). - Fixed CloudWatch metrics
serverdimension showing127.0.0.1for Amazon EFS and S3 Files mounts. Theknfsd-metrics-agentnow readsefs-utilsstate files from/var/run/efs/at scrape time to resolve the proxy loopback address to the real DNS name (e.g.<fs-id>.efs.<region>.amazonaws.comor<az-id>.<fs-id>.s3files.<region>.on.aws). - [EXPERIMENTAL] Added
examples/s3-filesTerraform example demonstrating Amazon S3 Files fronted by KNFSD proxy. Provisions S3 bucket with versioning, S3 Files filesystem, mount target, synchronization configuration, and required IAM roles/policies. - Added
FSID_DB_SUBNET_IDSvariable to thedatabaseandterraform-module-knfsdmodules. Callers using a non-default VPC can now pass a list of 2+ subnet IDs and the module will create theaws_db_subnet_groupautomatically. Mutually exclusive withFSID_DB_SUBNET_GROUP_NAME. Pre-apply validation enforces at least 2 unique subnets, inclusion ofvar.SUBNET, which must be in the same VPC asvar.SUBNET, and coverage of at least 2 availability zones within the AWS region. See FSID Database Options. Default VPC is still supported when both variables arenull(default). - Hardened
knfsd-fsiddagainst transient RDS IAM authentication failures caused by IAM policy propagation races on fresh deployments. Added SQLSTATE28000("PAM authentication failed") to the retryable error set inretry.go, and bounded the boot-timeCreateTableretry window to 90 secs via a newwithRetryDeadlinehelper (socket-handler retries remain at the default 5 min). AddedRestart=on-failure,RestartSec=10s,StartLimitBurst=3,StartLimitIntervalSec=600toknfsd-fsidd.service; worst-case cumulative retry time before systemd marks the unit failed is ~5 mins. - Added
iam_role_nameoutput to KNFSD proxy Terraform module (deployment/terraform-module-knfsd/outputs.tf) to allow external IAM policy attachments. - Pre-create the
knfsd/metricsCloudWatch log group inproxy-startup.shbefore startingknfsd-metrics-agentto avoidOperationAbortedExceptionwhen multiple scrapers concurrently callCreateLogGroupon first boot of first KNFSD instance. - Updated KNFSD Monitoring Dashboard to
v12. - Added
ENA-X(SRD) metrics toamazon-cloudwatch-agent.jsonfile. - Added
net_packets_recvandnet_packets_sentmetrics toamazon-cloudwatch-agent.jsonfile. - Added
ENA-X(SRD) metric widgets to CloudWatchmetricsdashboard. - Added support to CloudWatch
metricsdashboard to filter by differentudevnetwork interface names for different generation EC2 instance types. - Added Terraform validation to ensure selected
INSTANCE_TYPEis offered in the selected subnet's availability zone. - Rename references to
fsidd.socktoknfsd-fsidd.sockto be consistent (naming convention now matches:/run/knfsd-metrics.sock). - Added
ExecStopPost=toknfsd-metrics-agentsystemd service via AMI build file:proxy.serviceto remove the metrics socket file after the service stops. - Added
GOMEMLIMITenvironment variable toknfsd-metrics-agentsystemd service files:proxy.serviceandclient.serviceto limit the amount of memory available to the agent. - Updated
memory_limiterconfiguration inknfsd-metrics-agentconfigurationcommon.yamlfile to limit the amount of memory available to the agent to 512 MiB with a spike limit of 128 MiB. - Increased collection interval of
fscacheandnetfsmetrics from30sto1minknfsd-metrics-agentconfigurationcommon.yamlfile. - Added
rpc.mountd[]: can't stat exported dir /acme/home/<username>: Successsyslog message to known-issues documentation. - Swapped
pipforuvin.devcontainer/dev,.devcontainer/prod, andsetup-remote-vm.shscript for more performant Python package management. - Centralized
set -euxin the DockerfileSHELL [...]directive and removed per-command usage. - Refactored
setup-remote-vm.shscript to run asrootandubuntuuser, with the latter running user-level tools in a virtual environment. - Added
modernizelinter togolangci-lintconfiguration. - Fixed
modernizelinter warnings in multiple golang projects. - Added missing
${CI_DEPENDENCY_PROXY_DIRECT_GROUP_IMAGE_PREFIX}variable to GitLab CI configuration for PostgreSQL image ingo-knfsd-fsidd 4/5job. - Packer: Updated minimum required IAM permissions for Packer build process in README.md documentation.
- Packer: Removed redundant
apt-get installcall formakeandgccin20_post_build.shscript. - Packer: Added
retryandretry-delayto allcurlcommands in10_build.shand20_post_build.shscripts. - Packer: Wrapped all
git clonecommands in10_build.shand20_post_build.shwith agit_clonefunction to add retry logic. - Packer: Updated to
mdadmv4.6. - Packer: Updated to
rustv1.94.1. - Packer: Updated to
amazon-efs-utilsv3.1.0. - Refactored
.devcontainer/dev/Dockerfileto improve caching of Docker build layers and BuildKit cache mount performance. - Updated to Packer v1.15.1.
- Updated to Terraform
awsprovider v6.42.0. - Updated to Golang v1.26.2.
- Updated to Python v3.14.4.
- Minor Golang package updates.
v1.1.0-alpha.23 (March 13, 2026)
BREAKING CHANGES:
proxy-startup.shscript is now installed into the AMI via Packer and only executed via EC2 user data on every boot.BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Packer: Updated to Linux kernel v6.19.7-knfsd.
- Packer: Add
perfanalysis tool (excludingmanpages) to AMI to enable performance benchmarking and tuning. - Packer: Updated to use EC2 Spot instance types for build process to lower build cost (up to ~87% reduction) and dramatically increase capacity availability. AWS does not charge for an EC2 Spot instance if interrupted in the first hour.
- Packer:
proxy-startup.shscript is now installed into the AMI via Packer and only executed via EC2 user data on every boot. - Packer: Updated to use
tmpfsfor/mnt/buildand/tmpto improve build performance and remove the need for a persistent EBSgp3volume. - Packer: Applied
intel_idle.max_cstate=1 processor.max_cstate=1to GRUB boot parameters to limit CPU idle C-states to C1 to reduce interrupt/wake-up latency on supportedx86_64EC2 instance types. - Packer: Switch to using
cdn.kernel.orgendpoint for kernel source downloads to improve download reliability. lazytimemount option added tofscachemount inproxy-startup.shscript to only update times (atime, mtime, ctime) on the in-memory version of the file inode (reduces write load).- Updated to Golang 1.26.1.
- Updated to PostgreSQL v18.3.
- Updated to Terraform
awsprovider v6.36.0. - Improvements to CloudWatch
metricsdashboard layout and widget styling. - Updated KNFSD Monitoring Dashboard to
v11. - Packer: Pinned
amzn/amzn-driversENA driver toena_linux_2.16.1. - Minor Golang package updates.
v1.1.0-alpha.22 (February 27, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Packer: Updated to Linux kernel v6.19.4-knfsd.
- Removed
0001-nfsd-never-defer-requests-during-idmap-lookup.patchkernel patch that is now included in the v6.19.4 release. - Updated to Terraform
awsprovider v6.34.0. - Updated to Terraform
randomprovider v3.8.1. - Refactored
nfs.threadsmetric to usepgrep -c -x nfsdinstead ofprometheus/procfs/nfsto count the currently running number of NFS threads in preparation for Linux v7.0 kernel release. - Enhanced
proxy-startup.shwith dynamic memory management: addedcalculate_min_free_kbytesfunction to setvm.min_free_kbytesbased on total RAM, adjustedVFS_CACHE_PRESSURE, and refined kernel parameters for improved NFS performance. - Fixed bug in CloudWatch
metricsdashboard where the disk filesystem type was incorrectly set toxfsinstead ofext4. - Updated KNFSD Monitoring Dashboard to
v10. - Added explicit
EC2 Instance Connect Endpoint(EICE) support torun-fio-nfs.shandremote.shscripts to support private subnets (no public IP). - Added ability to provide custom EC2 keypair to
run-fio-nfs.shscript. - Enhanced
BATSunit tests forproxy-startup.shscript to test allsysctlsettings. - Minor Golang package updates.
v1.1.0-alpha.21 (February 23, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Updated to Ubuntu 24.04.4 LTS.
- Packer: Updated to Linux kernel v6.19.3-knfsd.
- Updated to Golang 1.26.0.
- Updated to PostgreSQL v18.2.
- Updated to Packer v1.15.0.
- Updated to
nfs-utilsv2.8.5. - Updated to Terraform AWS provider v6.33.0.
- Switched FS-Cache filesystem from
EXT4toXFSwith tunedmkfs/mountoptions, added block-device tuning (nomerges,read_ahead_kb) and VM sysctls (min_free_kbytes,compaction_proactiveness,dirty_ratio,swappiness) to reduce deadlock risk and improve NVMe cache performance. - Added KNFSD Test Plans for:
- Directory Listing
- Recovery Proxy
- Recovery Source
- Recovery Load Balancer
- Added
gosecuretoMakefileto run Go vulnerability scanning on all Go projects. - Added
gosecureGitLab CI jobs forsmoke-testsandtesting/examplesGolang projects. - Switched to using
golangDocker image for Go vulnerability scanning in GitLab CIgosecjobs. - Added
wait_for_capacity_timeout = "0"toaws_autoscaling_group.knfsd_asginterraform-module-knfsdto avoid rare ASG waiter false-negative failures. - Added
REMOVE_EMPTYfunction to CloudWatchSEARCHexpressions for FS-Cache Read & Write Throughput metrics in dashboard to remove anyNaNvalues. - Fixed bug in metric math expressions for
Cluster Network BandwidthandProxy Network Bandwidthwidgets in CW dashboard. - Added
diskio_read_timeanddiskio_write_timemetrics toamazon-cloudwatch-agent.jsonfile. - Added
I/O Requests: Waiting on Diskwidget to CloudWatch dashboard. - Added
Output NFS Filerto CloudWatch metrics dashboard to filter by Output NFS Filer(s), which might be different from the Source NFS Filer(s). - Removed
periodparameter from high-resolution CW dashboard widgets to use the automatically aggregated period. - Added
idparameter to all metric math expressions in CW dashboard to ensure deterministic label ordering within each widget. Label ordering is ignored whenstackedistruein a CW metric widget. - Improved some of the CW dashboard text descriptions.
- Aligned CW dashboard widget colours to be consistent.
- Updated KNFSD Monitoring Dashboard to
v9. - Added
fioandstress-ngpackages to KNFSD AMI to enable NVMe/NFS/FS-Cache performance testing. - Added
run-benchmark-nvme.shscript to.devcontainer/devfor NVMeinstance-storeperformance testing using FIO. - Added
run-fio-nfs.shscript to.devcontainer/devfor NFS/FS-Cache performance testing using FIO. - Added
create-source-files.fiofile to.devcontainer/dev/fiofor creating source files for NFS/FS-Cache performance testing using FIO. - Added
nfs-fscache-deadlock.fiofile to.devcontainer/dev/fiofor NFS/FS-Cache performance testing using FIO. - Exposed
FSX_STORAGE_CAPACITY,FSX_THROUGHPUT_CAPACITY, andNUM_NFS_THREADSTerraform variables to thefsx-zfsexample. - Packer: Updated README to clarify
var.SUBNETis required only if using a non-default VPC. - Packer: compile/install
mdadmfrom source into AMI to removemd: async del_gendisk mode will be removed in future, please upgrade to mdadm-4.5+warning fromdmesgoutput. - Minor Golang package updates.
v1.1.0-alpha.20 (January 30, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Packer: Switched to use compiled from source, Linux kernel v6.19.0-rc7 and NFS kernel patches for KNFSD AMI.
- Introduced
fscacheOpen Telemetryreceiver/componentto track the performance of the FS-Cache and Netfslib. See FS-Cache Metrics and Netfs Metrics for more information. - Added 37 x
NetfsLiband 24 xFS-Cachemetrics to CloudWatchmetricsdashboard. - Added
REMOVE_EMPTYfunction to CloudWatchSEARCHexpressions in metrics dashboard to remove anyNaNvalues. - Added
Total BWwidget to CloudWatch metrics dashboard to track the total bandwidth used by clients to all proxies in the ASG. - Added
Cluster Network Bandwidthwidget to CloudWatch metrics dashboard to track the network throughput of the entire cluster. - Consolidated the NFS v3 and NFS v4 CloudWatch metrics widgets.
- Updated KNFSD Monitoring Dashboard to
v8. - Fixed some dead/404 links in the documentation.
- Packer: Updated
hashicorp/packer-plugin-amazonto v1.8.0. - Packer: Created
/etc/amazon/ssmdirectory in build process to silence SSM agent log noise. - Updated to Golang 1.25.6.
- Updated to Terraform DNS provider v3.5.0.
- Updated to Terraform AWS provider v6.30.0.
- Minor Golang package updates.
v1.1.0-alpha.19 (January 9, 2026)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Downgraded default database instance type from
db.t4g.smalltodb.t4g.micro, reducing RDS database infrastructure cost by 50%. - CloudWatch metrics dashboard improvements, improved burst CPU credit balance/usage/unlimited-mode tracking on RDS DB instance.
- CloudWatch metrics: remove
swap_percent(unused), replacemem_used_percentwithmem_available_percent(memory available for use) inknfsd/ec2namespace. - Added
knfsd/nfs_clientsmetric to count the number of unique NFS client IP addresses connected to a KNFSD proxy. - Added new CW widget to track the number of EC2 instances (NFS clients) mounted to each KNFSD proxy.
- Introduced
nfsdOpen Telemetryreceiver/componentto track the performance of the KNFSD server. See KNFSD Server Metrics and Kernel NFS Server Statistics for more information. - Added
knfsd/nfs_packets_arrived,knfsd/nfs_packets_deferred,knfsd/nfs_sockets_enqueued,knfsd/nfs_threads,knfsd/nfs_threads_timedout, andknfsd/nfs_threads_wokenmetrics. - Added
fscdevicedimension todiskiometrics inknfsd/ec2namespace inamazon-cloudwatch-agent.jsonfile. - Refactored CloudWatch custom
metricsdashboard to usefscdevicedimension for certaindiskiometric filtering. - Increased collection interval of
diskiometrics from 30s to 10s inknfsd/ec2namespace inamazon-cloudwatch-agent.jsonfile. - Updated KNFSD Monitoring Dashboard to
v7. - Fixed Windows host machine being able to deploy the RDS DB in the
databasemodule. - Updated
prerequisitesdocumentation to declarebashandjqas being required which are already vendored in the.devcontainer/devand.devcontainer/prodenvironments. - Fixed issue where the AWS IAM role
AutoScalingServiceLinkedRoleneeds to be created once in a brand new AWS account when usingTRAFFIC_MODE="loadbalancer"in theterraform-module-knfsdmodule. - Updated to Terraform AWS provider v6.28.0.
- Added
provider_metato all Terraform AWS provider blocks withUSER_AGENTstring. - Minor Golang package updates.
v1.1.0-alpha.18 (December 12, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Added
SVC_RPC_PER_CONNECTION_LIMITvariable toterraform-module-knfsdmodule. This allows users to specify the number of RPC requests that the server will process in parallel from a single connection. Default:0(no limit). - Re-introduced
EXPORT_CIDRvariable toterraform-module-knfsdmodule. This allows users to specify custom CIDR blocks to use in the NFSD/etc/exports.d/knfsd.exportsfile. By default, the primary VPC CIDR block is used. For secondary VPC CIDRs, users must explicitly provide the full list via:EXPORT_CIDR. - Packer: Removed
multipath-toolspackage from AMI to reduce syslog noise frommultipathdservice, which is irrelevant to KNFSD instances on AWS. - Packer: Added log rotation with
sizelimit for/var/log/*.log,/var/log/syslog, and/var/log/journal/files. See rsyslog and 99-size-limit.conf for exact configuration. - Updated KNFSD Monitoring Dashboard to
v6. Lots of minor improvements. - Updated to Golang 1.25.5.
- Updated to Terraform AWS provider v6.26.0.
- Minor Golang package updates.
- Updated to Python v3.14.2.
- Updated to Psycopg3 v3.3.1.
v1.1.0-alpha.17 (December 2, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
BREAKING CHANGES:
var.EXPORT_CIDRhas been renamed tovar.VPC_CIDRand is nowtype = list(string)withdefault = []. Users who currently setEXPORT_CIDR = "172.31.0.0/16"must update toVPC_CIDR = ["172.31.0.0/16"]. When empty, the primary VPC CIDR block is used for security group rules and NFS exports. For secondary VPC CIDRs, you must explicitly provide the full list. For example:VPC_CIDR = ["172.31.0.0/16", "172.32.0.0/16"].BREAKING CHANGES:
var.ASG_EGRESS_CIDR_BLOCKhas been renamed tovar.ASG_EGRESS_CIDR.
- Major overhaul of CIDR handling across all modules. Multiple CIDR blocks can now be specified for security group rules and NFS exports. By default, the primary VPC CIDR block is used. For secondary VPC CIDRs, users must explicitly provide the full list via:
VPC_CIDR. - Terraform
databasemodule now supports cross-VPC access with VPC peering. - Pinned Linux HWE kernel to v6.14.0-36-generic.
- Substantial improvements to CloudWatch
metricsdashboard. KNFSD Monitoring Dashboard updated tov5. - Reduced default value for
NUM_NFS_THREADSfrom256to128interraform-module-knfsdmodule. - Added the
otelcol.Factories.Telemetryfield which is now required by OpenTelemetry v0.140.0 inknfsd-metrics-agent. - Removed unused VS Code extensions from
.devcontainer/dev. - Added
uvto.devcontainer/devfor Python package management. - Updated to Terraform AWS provider v6.23.0.
- Minor Golang package updates.
v1.1.0-alpha.16 (November 21, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Added
TCP_SLOT_TABLE_ENTRIESandTCP_MAX_SLOT_TABLE_ENTRIESvariables toterraform-module-knfsdmodule. These kernel tunables control the number of simultaneous RPC requests, per TCP connection, the proxy can send to the source filer. Default:128. - Reduced default value for
NUM_NFS_THREADSfrom512to256interraform-module-knfsdmodule. - Reduced default value for
VFS_CACHE_PRESSUREfrom100to1interraform-module-knfsdmodule. - Added
PROXY_AMI_OWNERSvariable toterraform-module-knfsdmodule. This allows you to specify the AMI owners to limit the AMI search. Default:["self"]. If your AMI is created by Packer in a different AWS account, you can specify the AWS account ID here. - Removed
owners = ["self"]from./examplesto simplify the examples. - Converted incorrect Terraform data type (string -> number) for
VFS_CACHE_PRESSUREandNCONNECTvariables interraform-module-knfsdmodule. - Added Terraform validation checks to ensure
VFS_CACHE_PRESSUREis between0and100, andNCONNECTis between1and16. - Refactored how metadata (IMDSv2) is retrieved during instance startup, improving reliability and reducing startup time.
- Ensure all services are stopped silently before configuration, preventing any potential conflicts with the startup process.
- Fixed a bug where the RAID array was not being reassembled correctly during KNFSD instance reboot.
- Refactored
proxy-startup.shto improve error logging and function stack tracing during KNFSD instance startup failures. - Added total execution time to
proxy-startup.shscript for benchmarking/debugging purposes. - Downgraded default database instance type from
db.t4g.mediumtodb.t4g.small. - Packer: run
cloud-init clean --logs --seedduring image build to ensure a clean state/logs in the AMI. - Ensure consistent shebang across all shell scripts in the project.
- Updated to Python v3.14.0.
- Updated to PostgreSQL v18.1.
- Updated to Terraform AWS provider v6.22.0.
- Minor Golang package updates.
- Removed pinned OpenShift API Golang dependency in
knfsd-metrics-agent. - Added parallelism (where feasible) to all Golang unit tests, reduced GitLab CI Golang jobs runtime by >50%.
v1.1.0-alpha.15 (November 13, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Added ARM support. Graviton EC2 instances can now be used to build & run KNFSD-File-Cache.
- Packer: Enabled parallel builds for both AMD64 and ARM64 architectures.
- Packer:
ARCHvariable can be set to["amd64"],["arm64"], or["amd64", "arm64"]to build only the specified architectures. Default:["amd64", "arm64"]. - Added
PROXY_AMIchecks interraform-module-knfsdroot module to validate the proxy AMI exists and uses the correctamd64/arm64architecture for the given instance type. - Added
PROXY_AMIchecks in./examplesto validate the proxy AMI exists and uses the correctamd64/arm64architecture for the instance type. - Fail earlier if the
db_setup.pyLambda function fails to execute successfully. - Updated to Terraform AWS provider v6.20.0.
- Updated to
nfs-utilsv2.8.4. - Minor Golang package updates.
v1.1.0-alpha.14 (November 6, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Packer: Refactored pre-build & post-build scripts to be Packer variables, similar to the Terraform module.
- Packer: Added
CUSTOM_PRE_BUILD_SCRIPTandCUSTOM_POST_BUILD_SCRIPTvariables to allow for custom build steps. - Packer: Added
IAM_INSTANCE_PROFILEvariable to allow for custom IAM instance role to be used during image build. - Updated to Golang 1.25.4.
- Minor Golang package updates.
- Fixed Open-Telemetry upstream golang dependency package issue in
knfsd-metrics-agent. - Added
proxy.golang.orgto GitLab CI jobs. - Enhanced
Makefileto supportpre-commit autoupdate. - Added AWS SSM agent to
remote-sshandremote-dockerinstall scripts.
v1.1.0-alpha.13 (November 3, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Packer: Fixed bug in
20_post_build.shscript where/etc/machine-idfile must exist for systemd dependencies at boot. - Packer: Added
proxy.golang.orgtoGOPROXYenvironment variable to handle situations where a VCS based git repo is unavailable, causing the image build process to fail (continue to usedirectonly in the devcontainer/build environment to ensure golang dependencies/versions are working correctly). - Packer: Updated
hashicorp/packer-plugin-amazonto v1.6.0. - Updated to Terraform AWS provider v6.19.0.
- Minor Golang package updates.
- Improved documentation in various places, including nfs-client-setup.md.
v1.1.0-alpha.12 (October 27, 2025)
BROKEN: Do NOT use this release.
- Updated
metricsdocumentation. - Added
docs/nfs-client-setup.mddocumentation to explain recommended client setup for KNFSD. - Updated
THIRD-PARTY-LICENSESfile. - Improved
update-version.shscript to update all version strings in the repository. - Minor Golang package updates.
- Updated to KICS v2.1.15.
- Updated to Python v3.13.9.
- Removed unused terminals in
.devcontainerfor improved performance. - Silenced false-positive in
semgrepcheck.
v1.1.0-alpha.11 (October 24, 2025)
BROKEN: Do NOT use this release.
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Pinned Linux HWE kernel to v6.14.0-29-generic due to bug.
- Updated default
INSTANCE_TYPEtoi3en.6xlargeinterraform-module-knfsdmodule and all examples. - Updated default
INSTANCE_TYPEtoi3en.12xlargeinfanoutexamples. - Updated to Terraform AWS provider v6.18.0.
- Updated to Golang 1.25.3.
- Minor Golang package updates.
- Added missing NFSv4 file operations widgets to CloudWatch
metricsdashboard. - Added a tutorial: "Deploy a kernel space NFS caching proxy on AWS". See README for more information.
- Cleaned up log messaging in
proxy-startup.shscript for custom pre/post startup scripts. - Fixed bug in custom pre/post
proxy-startup.shscript handling where double-quotations were not being handled correctly inside inline bash commands or referenced shell script files. - Packer: Added
missingokandnotifemptytoknfsd-logrotate.conf. - Packer: Purge
/etc/machine-idfile to ensure unique machine-id is generated during first-boot. - Added network throughput metric to CloudWatch
metricsdashboard.
v1.1.0-alpha.10 (October 9, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Added Terraform
metricsmodule to deploy a custom Amazon CloudWatch dashboard. See README, metrics, and client-metrics documentation. - Flattened and minimised the dimensions of all custom metrics.
- Fixed bug in Golang
knfsd-metrics-agentpreventingnfsiostatandmountmetrics from being published. - Refactored Open-Telemetry dimension configuration across
common.yaml,proxy.yaml, andclient.yaml. - Enhanced
proxy-startup.shto handle different Nitro block device names depending on NVMe, EBS, RAID0 configuration at initial KNFSD instance startup only. - Updated to Terraform AWS provider v6.15.0.
- Updated to Golang 1.25.2.
- Updated KICS to 2.1.14 (and silenced false-positive).
- Minor Golang package updates.
- Updated to Python 3.13.8 (awaiting Python 3.14 support in AWS Lambda runtime).
- Fix initial error with
proxy-startup.shstartup order with KNFSD metrics agent andnfsd. - Tweak
golangci-lintyaml config to ignoremisspellfalse-positive ontestcert.goin CI pipeline. - Fixed
semgrepbug via updating to 1.137.0. - Updated Amazon EBS
gp3settings interraform-module-knfsdthat increase the maximum size and provisioned performance as per announcement. - Reduce TF variable:
ROOT_DISK_SIZEfrom 100GB to 20GB for KNFSD instance boot volume (5x cost saving on EBSgp3used). - Added WARNING to
fanoutdocumentation: Ensure the fanout EC2INSTANCE_TYPEis at least 2x-8x more powerful than the cluster EC2INSTANCE_TYPE(use a larger size).
v1.1.0-alpha.9 (September 14, 2025)
- Updated to Terraform AWS provider v6.13.0.
- Updated to Packer v1.14.2.
- Updated to KICS v2.1.13.
- Updated to Golang 1.25.1.
- Minor Golang package updates.
- Fixed issue where the CloudWatch log group for the
static-ipLambda function can be re-created by an EC2 instance terminating slowly after its ASG is deleted during a Terraform destroy. - Refactored the handling of the secondary
static-ipENI when an EC2 instance is terminated for any reason other than a scale-in event. - Exposed Terraform
KNFSD_NODESandINSTANCE_TYPEvariables to thefsx-zfsexample. - Refactored
proxy-startup.shto be stateless. - Added support for KNFSD machine reboot,
/var/cache/fscachedata persists between reboots (shutdown not supported). - KNFSD specific NFS exports are now stored in
/etc/exports.d/knfsd.exports, leaving default/etc/exportsuntouched. - Ensure
resourcesdirectory is writable by all users in../deployment/database/resources/docker-build.sh.
v1.1.0-alpha.8 (September 3, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Packer: due to an emerging bug in
hashicorp/packer-plugin-amazonv1.4.0, pin the plugin version via pessimistic constraint operator to v1.3.10. - Revert Docker Lambda DB function to exclusively use amd64 (x86_64) architecture to work across all platforms by default.
- Refactored CloudWatch JSON configuration file for CW log storage and CW appended dimensions.
- Minor Golang package updates.
- Updated Terraform provider.
- Added Packer plugin caching to dev/prod .devcontainer environment.
- Added ability to use specific AMI-id when provisioning a remote-ssh EC2 instance.
- Added
KNFSD_REMOTE_SSH_IAM_PROFILE_NAMEsupport todev.devcontainer for remote-ssh into EC2. - Added helper script to generate AWS region names for metrics dashboard.json file.
- Exclude pretty-format-json formatting of
dashboard.jsonfile from pre-commit hook. - Added
make image&make image-debugsupport to build Packer AMI via Makefile alias. - Exposed
FSID_MODEas a variable to thefsx-zfsexample. - Removed unused OTEL packages from
knfsd-metrics-agentGolang module.
v1.1.0-alpha.7 (September 2, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Updated to PostgreSQL v17.6.
- Minor Golang package updates.
- Updated to Golang v1.25.0.
- Updated to Python v3.13.7.
- Updated Terraform providers.
- Add Docker "buildx" CLI argument for cross-platform builds.
- Enhance Docker image inspect command to support multi-platform images.
v1.1.0-alpha.6 (July 22, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Added support for Linux v6.14 kernel, including NFS server, client and
FS-Cacheimprovements. - Minor Golang package updates.
- Packer: pinned version of
rustandefs-utils. - Packer: increased EBS root volume size from 8 GB to 10 GB.
- Packer: decreased EBS temp volume size from 50 GB to 20 GB.
- Packer: fixed bug preventing the
gobuild cache from being global within the build script. - Packer: updated Packer min version to v1.13.1.
- Packer: updated
amazon-ebsplugin min version to v1.3.9.
v1.1.0-alpha.5 (July 18, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Minor Golang package updates.
- Minor Terraform provider version updates.
- Refactored
knfsd-fsiddto always use a newiam-authTOKEN for a new database connection. - Added debug logging to
knfsd-fsiddto validate the local database cache is working as expected. - Added initial metrics changes to OTEL
*.yamlconfig files.
v1.1.0-alpha.4 (July 13, 2025)
BREAKING CHANGES:
var.ASSOCIATE_PUBLIC_IP_ADDRESSis nownullby default inimage.pkrvars.hcl. See Packer: Security Group Usage Scenarios for more information.
- Fixed a typo in OTEL
common.yamlconfig file. - Fixed a bug when
var.ASSUME_ROLE_ARNisnull(default) during deployment. - Packer: added
var.SECURITY_GROUP_IDinimage.pkrvars.hclto use an existing security group during image build. Default:"". - Packer: added
var.SECURITY_GROUP_IDSinimage.pkrvars.hclto use multiple existing security groups during image build. Default:[]. - Packer: added
var.TEMPORARY_SECURITY_GROUP_SOURCE_CIDRSinimage.pkrvars.hclto allow access from a list of CIDR blocks during image build. Default:[]. - Packer: added
var.TEMPORARY_SECURITY_GROUP_SOURCE_PUBLIC_IPinimage.pkrvars.hclto allow access from the public IP address of the machine running Packer during image build. Default:true.
v1.1.0-alpha.3 (June, 2025)
BREAKING CHANGES: Ensure AMI is rebuilt by Packer.
- Added
var.ASSUME_ROLE_ARNto allow for role assumption for Terraformlocal-execprovisioners. - Enabled Auto-Scaling (scale-up only) for the
loadbalancermodule. - Enabled OpenTelemetry metrics for the KNFSD proxy.
- Amazon CloudWatch metrics & logs are grouped by
knfsd/prefix. - Added
fsx-zfs-fanout-dns-rrexample to demonstrate how to use theterraform-module-knfsdmodule with an Amazon FSx for OpenZFS file system in afanout/dns-round-robinarchitecture. - Renamed
fsx-zfs-fanoutexample tofsx-zfs-fanout-loadbalancer. - Extended
deletetimeout during TerraformdestroyforAutoScalingGroupfrom 10m to 20m. - Fixed a bug in Eventbridge rules for
dns_round_robinmodule where the rules were not being created with unique names per cluster, causing a conflict in thefanoutarchitecture. - Fixed a bug in
dns_round_robinmodule where secondary ENI TAGknfsd-file-cache:instance-idcould be misrepresented in anec2.describe_network_interfacesfilter. - Split the default FQDN for
dns_round_robinmodule into two parts for Amazon Route 53:name=knfsdandzone=<PROXY_BASENAME>.aws.internal., ensuring unique zone names per cluster deployment. - Refactored
DNS_NAMEto allow users to specify their own private FQDN for the KNFSD proxy cluster. - If
var.DNS_NAMEis""(default), a private DNS zone (aws.internal.) is created, and A or CNAME record(s) (knfsd.<PROXY_BASENAME>.aws.internal.) are created via the Amazon R53 service. - If
var.DNS_NAMEis a FQDN, including trailing dot.(R53 private zone already exists), then A or CNAME record(s) (<CUSTOM_NAME>.<CUSTOM_DOMAIN>.) are created in the existing Amazon R53 zone. - Removed
var.PRIVATE_HOSTED_ZONEfrom all modules. - Added 60m timeout to
status.tfcheck to prevent infinite loops during deployment. - Minor Golang package updates.
- Fixed
proxy-startup.shconflict betweenfsiddandknfsd-fsiddservice, causing RDS database to not be used, whenFSID_MODE="external". - Enhanced the
fsx-zfsexample to deploy additional ZFS volumes and demonstrate the use ofEXPORT_HOST_AUTO_DETECTfeature (showmount), together with NFS v3 for performance. - Increased GitLab CI job
Trivytimeout to 10 minutes. - Added explicit support for
--regionin theawscalls via IMDS retrieval on the EC2 instance within theproxy-startup.shscript. - Added
fsx-netappexample to demonstrate how to use theterraform-module-knfsdmodule with an Amazon FSx for NetApp ONTAP file system in adns-round-robinarchitecture. This example uses the NetApp REST API to automatically discover, filter and configure exports. - Added documentation for GitLab-CI and Pre-Commit.
- Improved
proxy-startup.sh'cold' startup time from 281 seconds to 38 seconds (i3en.3xl), ~86% quicker. - Added timestamp to each stage of the Packer image build process.
- Consolidated log/metrics group names for CloudWatch & OpenTelemetry.
- Added Terraform AWS provider configuration to all
./examplesmodules. - Added new
./examplesto be cached in GitLab-CI pipeline. - Reduced default instance type from
i3en.6xlargetoi3en.3xlargein theterraform-module-knfsdmodule. - Updated
hashicorp/awsprovider to v6.0.0. Ensure youterraform init -upgradeto ensure you are using the correct version of the provider. - Added timestamp to each section of the
proxy-startup.shscript to measure startup timings. - Added
fsx-zfsexample to demonstrate how to use theterraform-module-knfsdmodule with an Amazon FSx for OpenZFS file system in adns-round-robinarchitecture. - Added
fsx-zfs-fanoutexample to demonstrate how to use theterraform-module-knfsdmodule with an Amazon FSx for OpenZFS file system in afanout/load-balancerarchitecture. - Added note to the
efsexample that Amazon EFS does not support being re-exported more than once, so does not support thefanoutfeature. - Removal of
var.REGIONfrom all modules. AWS Region is now derived from the providedvar.SUBNET. Can be overridden with AWS provider configuration in the root module. - Remove AWS provider configuration from Terraform root module (no longer a legacy module).
- Removal of VPC Endpoints from Terraform module. See VPC Endpoints for detailed setup instructions if required.
- Renamed
gitlab-ci.ymltogitlab-ci-aws.ymlto avoid conflicting with a customer'sgitlab-ci.ymlfile. - Minor software version updates.
- Updated
THIRD-PARTY-LICENSESfile for reference. - Updated to Packer v1.13.1.
var.EXPORT_CIDRnow defaults to""(VPC CIDR ofvar.SUBNETis used if not specified).var.ENABLE_STATUS_CHECKadded to enable the status check that waits for all EC2 instances to be KNFSD status:readyduring Terraform deployment. Must betrueforfanoutdeployments.var.FSID_DATABASE_CONFIGis now a JSONmapof key/value pairs that can be used to override the default FSID database configuration (used infanoutdeployments and when you want to reuse the database from a previous deployment).output.database_confighas been added to theterraform-module-knfsdmodule. It is amapof key/value pairs that can be used to override the default FSID database configuration (used infanoutdeployments).output.database_iam_policyhas been added to theterraform-module-knfsdmodule. It is an ARNstringthat can be used to attach the IAM policy to the KNFSD proxy instances.output.cluster_readyhas been added to theterraform-module-knfsdmodule. It is abooleanthat can be used withvar.ENABLE_STATUS_CHECKto wait for the KNFSD cluster and EC2 instances to be ready before deploying downstream resources.output.autoscaling_group_security_group_idhas been added to theterraform-module-knfsdmodule.null_resource.trigger_lambda_after_rdsnow explicitly targets the AWS--regionof the RDS instance.- Fanout documentation updated to reflect the new settings.
- Prerequisites documentation updated to reflect removal of VPC Endpoints.
- Fixed bug where Network Load Balancer target groups were not being created when
var.TRAFFIC_MODEwas set toloadbalancer. - Added additional IAM policy for EC2 instance "status" tagging.
- Fixed bug where
var.NFS_PORTSwas not being passed to theloadbalancermodule from theterraform-module-knfsdmodule. - Added
knfsd-file-cache:statustag to deployed EC2 instances for real-time status checking during deployment of a KNFSD cluster. - Updated
validations.tfto account forvar.FSID_DATABASE_CONFIGbeing a JSONmapof key/value pairs. - Secondary ENIs created for
dns_round_robindeployments now have aknfsd-file-cache:versiontag. proxy-startup.shnow updates theknfsd-file-cache:statustag to track the status of the proxy after it has started.readyis set after the proxy has successfully completed the startup process anderror: failed to start proxyis set if the proxy fails to start.proxy-startup.shonly attempts to mount Amazon EFS source server once, instead of three attempts (EFS helper utility already hard-wired to attempt to mount the EFS source server three times).check-startup.mddocumentation updated to reflect the newknfsd-file-cache:statustagging system for real-time status viewing in the AWS Console during deployment.known-issues.mddocumentation added entry to explain whyshowmountfails withclnt_create: RPC: Program not registeredwhen usingEXPORT_HOST_AUTO_DETECT.- Packer: added
var.ASSOCIATE_PUBLIC_IP_ADDRESSinimage.pkrvars.hclto force public IP address association during image build. Default:true. - Packer: added new CloudWatch EBS metrics to
amazon-cloudwatch-agent.jsonto monitor EBS volume performance.
v1.1.0-alpha.2 (May, 2025)
- Initial alpha release of KNFSD-File-Cache